How to enable GitHub Actions' immutable subject claims for OIDC and Azure
You may have read previous posts where I documented my attempts to get rid of Personal Access Tokens, Client Certificates and other permanent secrets. And if so, you're likely at least somewhat familiar with OIDC.

You may have read previous posts where I documented my attempts to get rid of Personal Access Tokens, Client Certificates and other permanent secrets. And if so, you're likely at least somewhat familiar with OIDC.
In the past you'd create a new App Registration in Azure, then set a Federated Credential on it and would copy the owner and repository name. Then Azure will let GitHub authenticate on your behalf using those fields in the claim.
There is one drawback to this, however. When you organization or repository is ever deleted, renamed or transferred, the App Registration will have a dangling credential. Anyone with the ability to create a new repo under the same name can regain access to that App Registration if they know the Client ID, Tennant ID and Subscription ID.
To prevent this from happening GitHub added support for adding the Owner ID and Repository ID into the subject claim. These values uniquely identify the repository and will prevent a takeover.
Before
If your repository is currently using OIDC, you may first need to enable "Use Immutable Subject Claim", or your claim prefix will only contain the names of the repository:
repo:jessehouwing/azdo-marketplace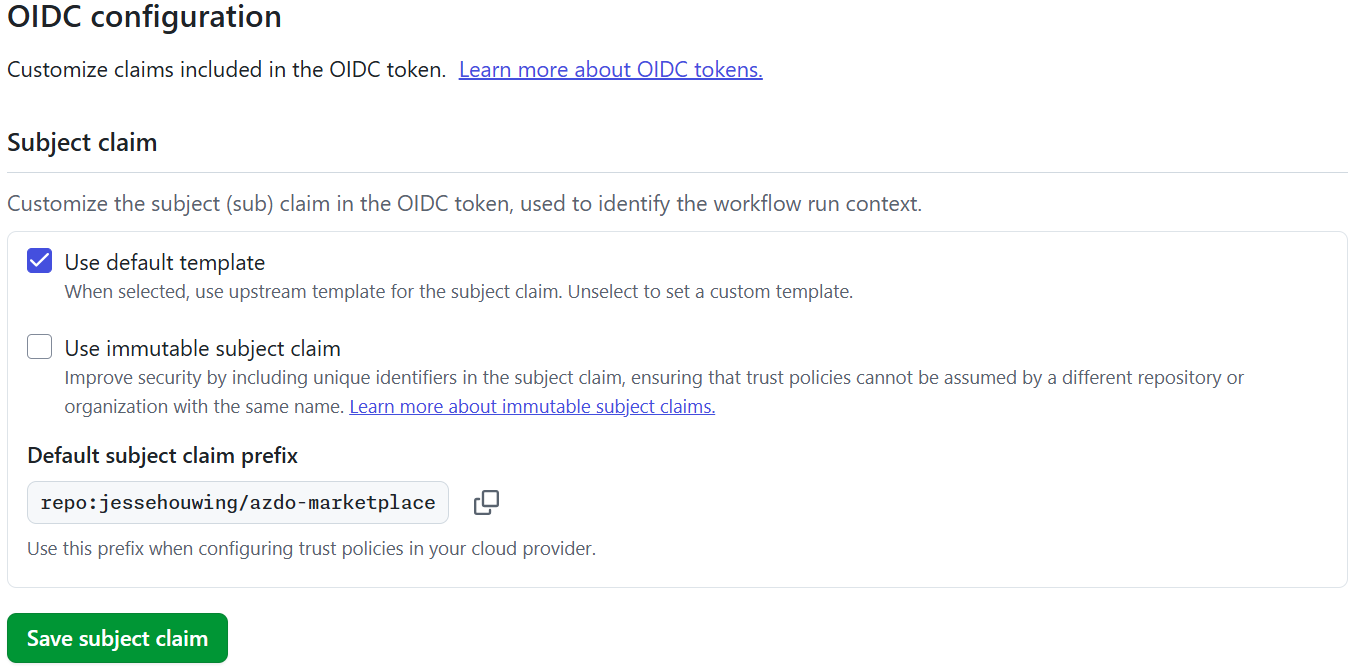
After
After enabling the "Use Immutable Subject Claim", you will see that the owner id and repository id have been added to the claim prefix:
repo:jessehouwing@4173387/azdo-marketplace@1158033287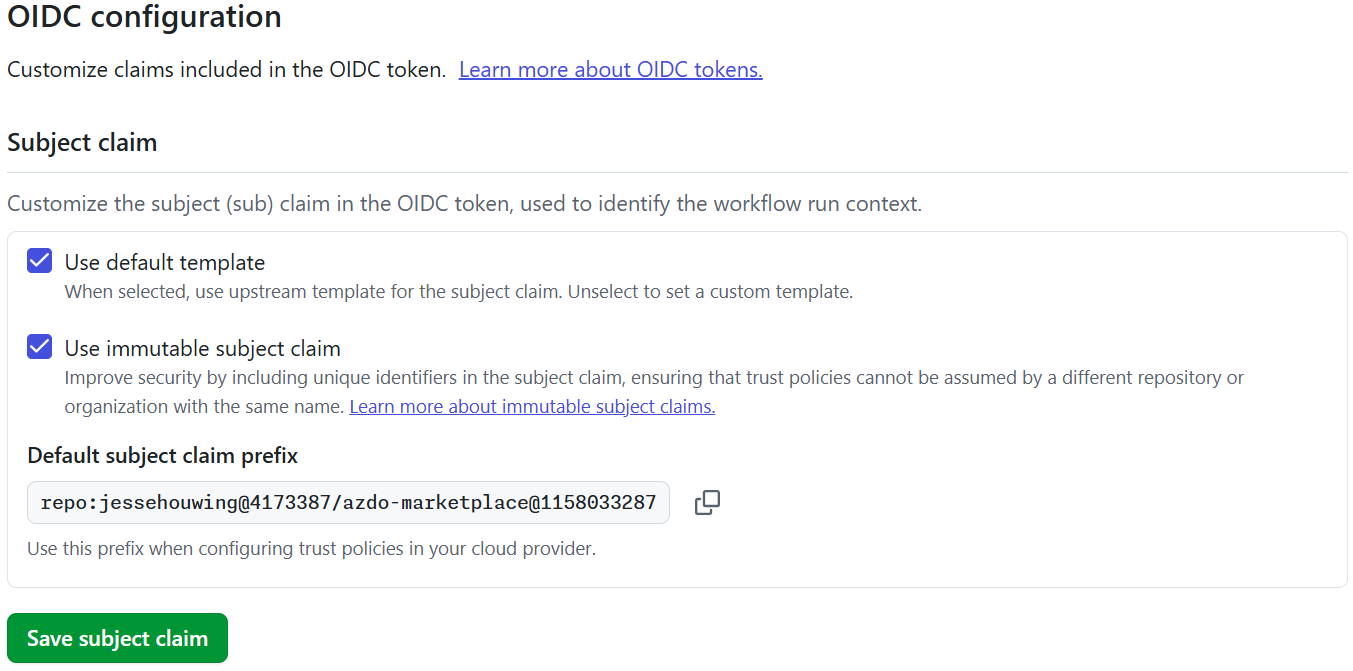
Retrieving the identifiers
If you need these values to use in automation, you can easily query them using the API:
> gh api repos/jessehouwing/azdo-marketplace --jq '{repo_name: .name, repo_id: .id, owner_name: .owner.login, owner_id: .owner.id}'

{
  "owner_id": 4173387,
  "owner_name": "jessehouwing",
  "repo_id": 1158033287,
  "repo_name": "azdo-marketplace"
}
GitHub Enterprise
If your repository is part of a GitHub Enterprise, you can set additional policies to include the Enterprise in your subject claim as well:
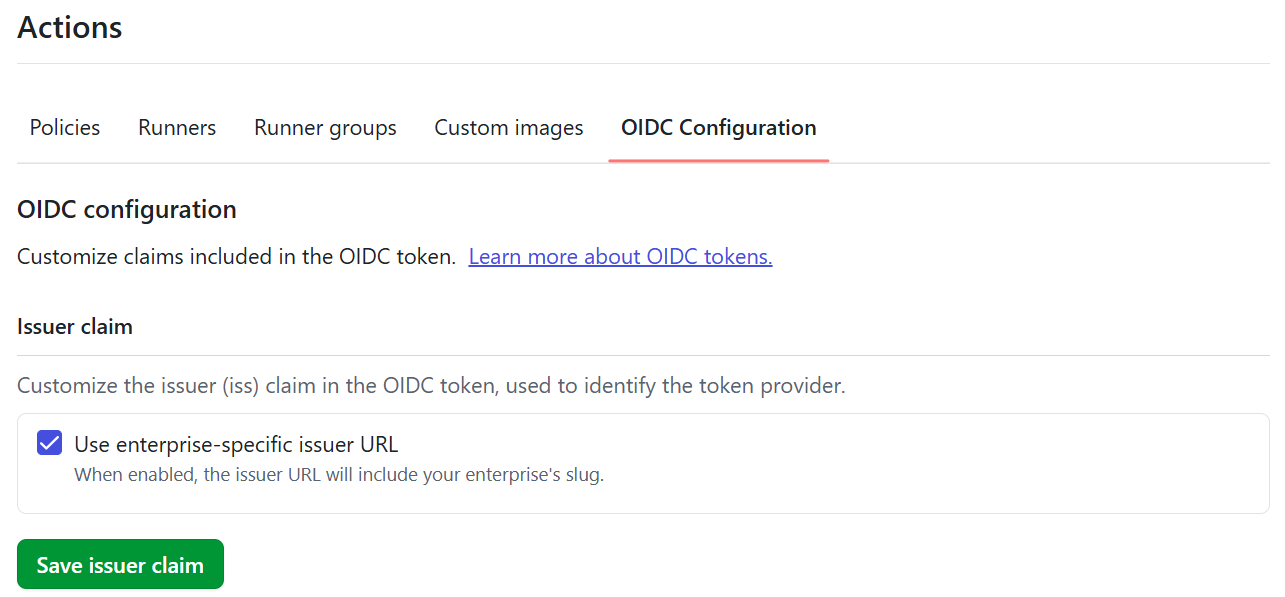
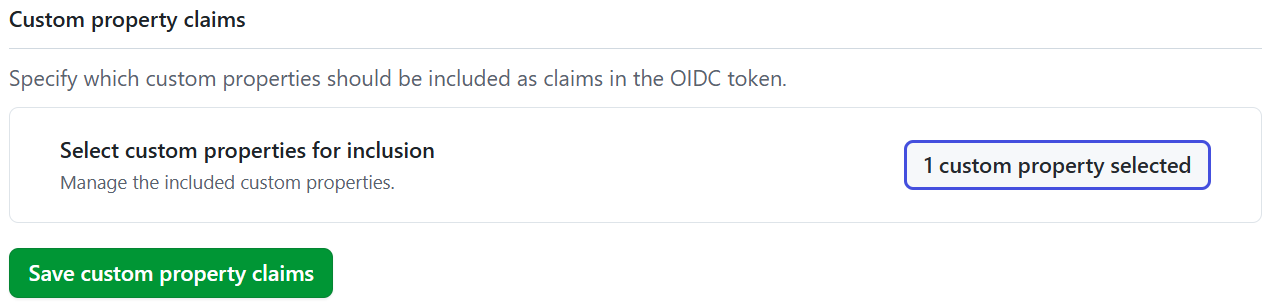
And include custom repository properties. This is a very useful feature to enable specific claims for multiple repositories at once. For example, you could set a environment: dev custom property on all repositories, which could grant all of these repos access to a Service Principal in Azure through a single federated credential.
The Azure Side
On the Azure side 2 new inputs have appeared, one for owner id and one for repository id:
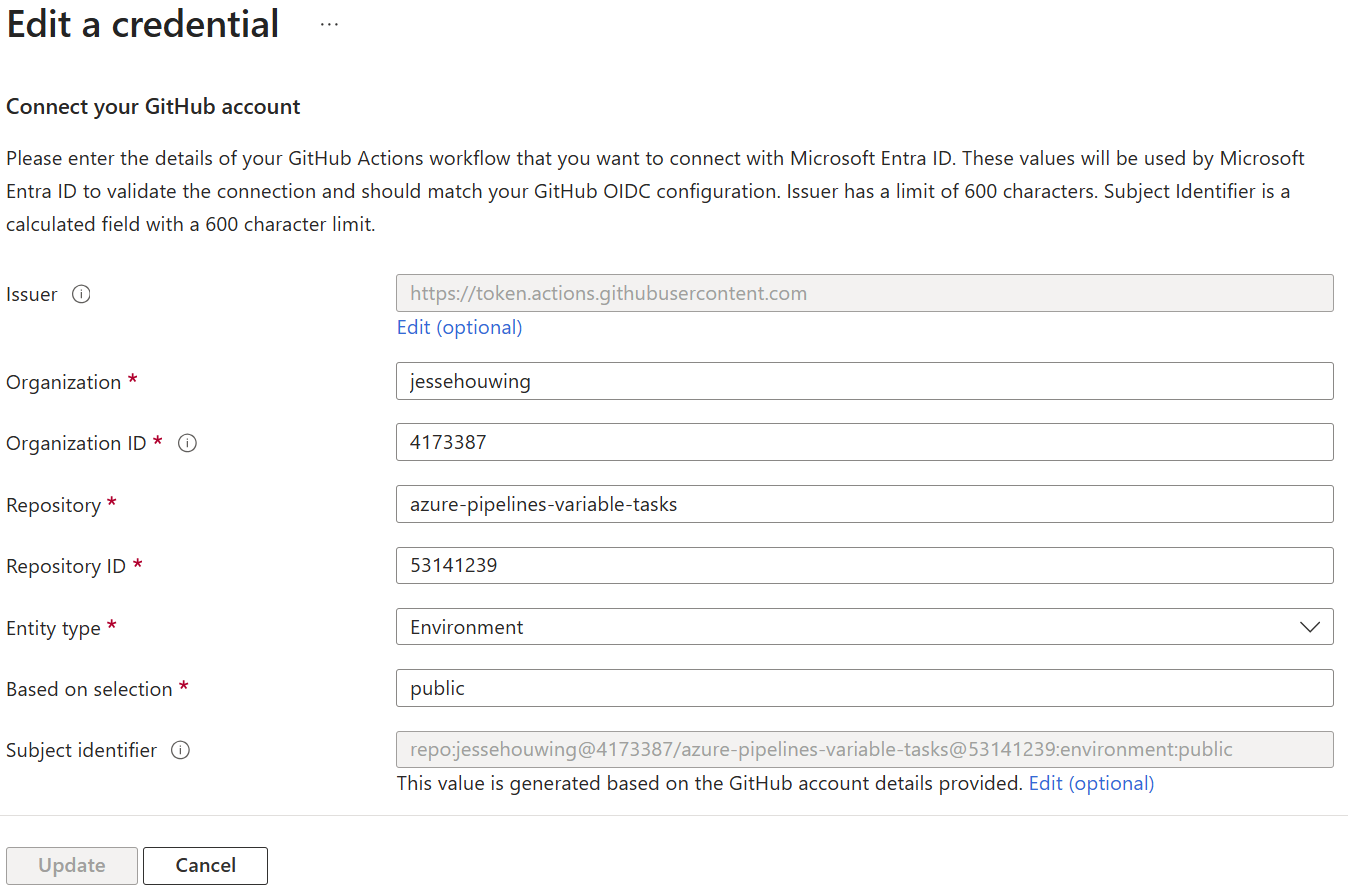
You should set these values before enabling Immutable Subject Claims.
If you want to use the enterprise claim or custom repository properties, you need to edit the Subject Identifier manually and supply your own format and adding the custom property by prefixing it with repo_property_name:value.